01
Trace
Label the origin of everything the agent sees: SYSTEM, USER, AGENT or RETRIEVED_CONTENT.
SENTINEL is a security proxy for MCP. It tracks where every tool result came from, and refuses the actions you guard when their data came from untrusted content. Even when the attack got past your content filter.
pip install "sentinel-prox>=0.2.2"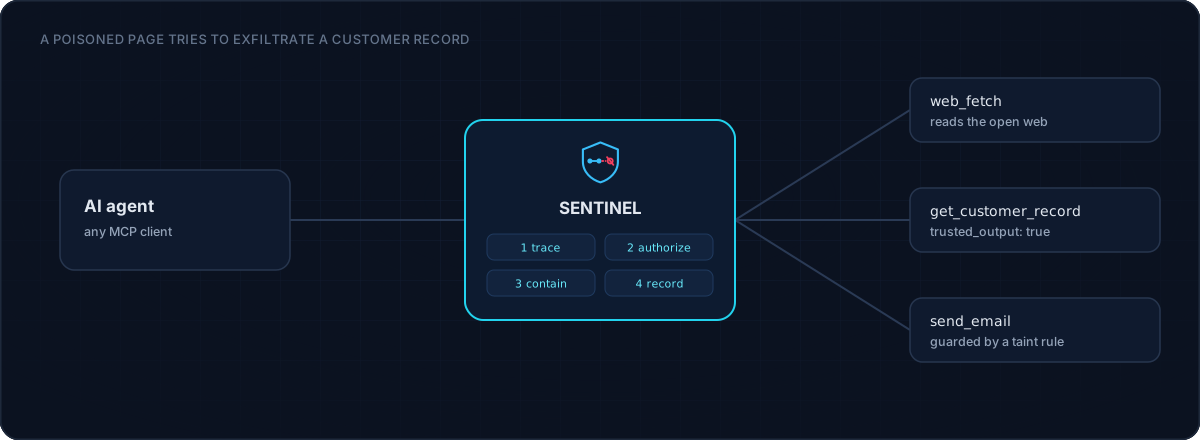
get_customer_recordALLOW
Allowed. The records service is marked trusted, so nothing is tainted yet.
web_fetchALLOW
Allowed, but the page it returns is labelled RETRIEVED_CONTENT.
send_emailBLOCK
Refused before it runs: its lineage includes the page, whatever the page said.
The problem
An attacker hides an instruction in content your agent will read: a web page, a document, a ticket. Content filters scan the text, and no filter catches everything. When one misses, the instruction runs with the agent's full privileges.
SENTINEL judges each action by where its data came from. Rewording or obfuscating the injection does not change that.
Read the full story →block-untrusted-originRETRIEVED_CONTENTNothing was sent. The agent got a tool error, and the attack is on record.
The bundled demo's data. The record is a labelled fake.
How it works
To your agent, SENTINEL is an ordinary MCP server. To your tools, it is the only client they ever see.
01
Label the origin of everything the agent sees: SYSTEM, USER, AGENT or RETRIEVED_CONTENT.
02
Your policy decides each call from that lineage. Deny-only rules, deny-overrides, unknown tools denied.
03
A trust score drops on denied calls and other signals, and can quarantine the agent.
04
Each decision becomes an immutable span. Replay a run, or export it as JSONL for a SIEM.
Observability
Blocks at WARNING, allowed calls at INFO, each with the trace id that ties it to the full forensic record.
--log-format json for your aggregatorBuilt for security teams
Small, explicit rules over a precise model of where data came from.
Every message and tool result carries a trust label. An action's provenance is the set of labels over its whole ancestry, never just the latest step.
YAML compiled to a typed condition tree. Unknown tools are denied until you write a rule.
send_email:
  rules:
    - id: block-untrusted-origin
      deny_if: "RETRIEVED_CONTENT in
        effective_provenance"
Attacks that arrive in a tool's definition never reach the agent.
Immutable spans, with arguments and results redacted before they are stored.
Enforcement is local and identical everywhere. Paid Azure services are optional upgrades.
Read before you deploy
SENTINEL is beta software. Each limitation changes what it protects you from, so they are documented, with their consequences, before anything else.
Status and limitations →No agent code changes. No paid services. Five commands from install to enforcement.
pip install "sentinel-prox>=0.2.2"